The Maintenance Nightmare: Why Manual Docker Updates Fail in HomeLabs
Managing two or three Docker containers is easy. You SSH into your host, run a quick pull, recreate the container, and get on with your day. Fast forward six months. Your single mini PC now hosts twenty microservices—Pi-hole for DNS filtering, Plex, Nginx Proxy Manager, paperless-ngx, and multiple databases.
At that scale, manual patching falls apart fast. Containers often sit unpatched for 90 days or more, leaving known CVEs wide open on your local network. Or worse, you log in late on a Sunday night and pull new tags across all your Compose stacks. By Monday at 7:00 AM, half your services are throwing 502 errors because an upstream maintainer pushed a breaking database schema migration without warning.
Blind automation causes outages, but doing everything by hand wastes hours. The solution is simple: automate minor, stateless updates quietly, leave stateful services alone, and push instant status alerts straight to your phone.
Core Concepts: How Watchtower Works (and How to Avoid Breaking Stacks)
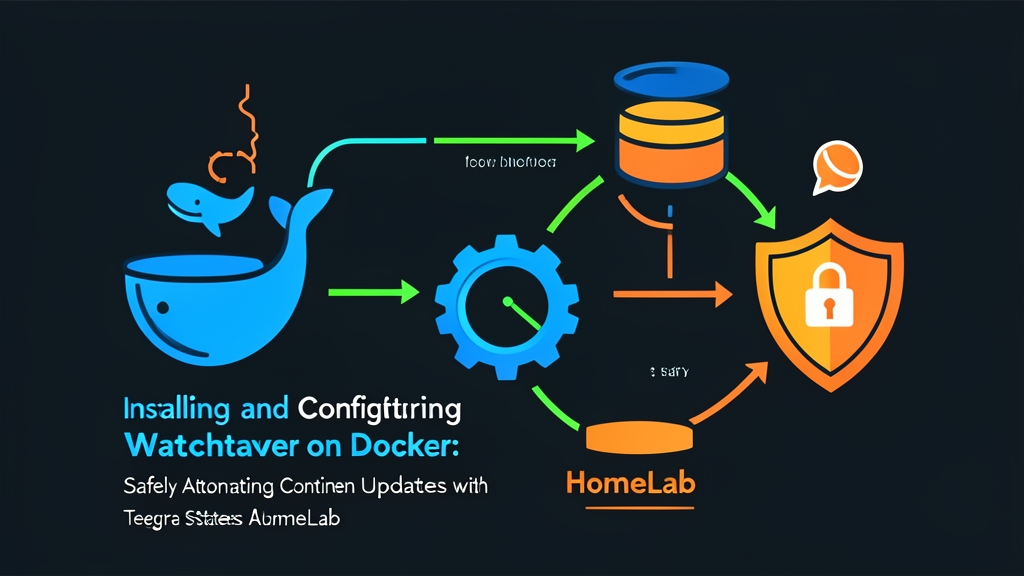
Watchtower runs as a lightweight Docker container that inspects your local engine through the Docker daemon socket (/var/run/docker.sock). At set intervals, it checks remote registries—like Docker Hub, GitHub Container Registry (ghcr.io), or a local Harbor instance—comparing your running image digest against the latest remote hash.
When it spots a fresh digest, Watchtower handles the transition through four steps:
- Pulls the new image digest down to your host storage.
- Sends a graceful stop signal (
SIGTERM) to the active container, waiting up to 10 seconds (by default) for clean shutdown. - Recreates the container with its exact original configuration—preserving ports, volumes, custom networks, environment variables, and restart policies.
- Drops the old dangling image layers to prevent unneeded image bloat on your SSD.
The goal is not to update everything automatically. The real trick is setting up firm guardrails.
Stateless tools like Cloudflare Tunnels, Whoogle, or Uptime Kuma can update automatically without incident. But stateful workloads like Nextcloud, Vaultwarden, or production PostgreSQL 15 instances should never update unattended. A surprise major version bump can instantly corrupt data directories or lock you out of your password vault.
The Opt-In Architecture (Label Filtering)
Out of the box, Watchtower monitors and updates every container attached to the Docker daemon. That default behavior is a disaster waiting to happen. To stay safe, run Watchtower in opt-in mode by setting WATCHTOWER_LABEL_ENABLE=true. Watchtower will ignore every service on your server by default. It touches a container only if you explicitly tag it with the label com.centurylinklabs.watchtower.enable=true.
Hands-on Practice: Deploying Watchtower with Docker Compose and Telegram
Step 1: Set Up Your Telegram Notification Channel
Before launching Watchtower, set up a private Telegram bot. It will deliver build digests, failure warnings, and update summaries directly to your chat.
- Open Telegram, search for @BotFather, and send
/newbot. - Pick a display name and a unique username ending in
bot. Copy the generated HTTP API Token (for example,7123456789:AAEk9_exampleTokenStringXYZ123). - Open your new bot’s profile in Telegram and press Start to open the conversation.
- Find your personal numerical Telegram ID. Message @userinfobot and send
/start. Note down the returned Id (for example,987654321).
Step 2: Prepare Your Directory and Docker Compose File
Create a dedicated folder for Watchtower on your host system:
mkdir -p ~/homelab/watchtower && cd ~/homelab/watchtower
nano docker-compose.yml
Paste the production configuration below. Note that Watchtower requires write access to docker.sock to stop, delete, and recreate containers. We set a 6-field cron schedule for 4:00 AM daily, enable dangling image pruning, and route notifications through Shoutrrr:
services:
  watchtower:
    image: containrrr/watchtower:latest
    container_name: watchtower
    restart: unless-stopped
    volumes:
      # Write access is required to restart and recreate containers
      - /var/run/docker.sock:/var/run/docker.sock
    environment:
      - TZ=America/New_York
      # Opt-in mode: update only containers with watchtower.enable=true
      - WATCHTOWER_LABEL_ENABLE=true
      # Prune old images after pulling replacements to save disk space
      - WATCHTOWER_CLEANUP=true
      # Restart the original container if the new deployment fails
      - WATCHTOWER_ROLLING_RESTART=true
      # 6-field Cron: Sec Min Hour Day Month DayOfWeek (Runs daily at 04:00:00)
      - WATCHTOWER_SCHEDULE=0 0 4 * * *
      # Notification engine configuration via Shoutrrr
      - WATCHTOWER_NOTIFICATIONS=shoutrrr
      - WATCHTOWER_NOTIFICATION_URL=telegram://7123456789:AAEk9_exampleTokenStringXYZ123@telegram?channels=987654321
      - WATCHTOWER_NOTIFICATIONS_LEVEL=info
      - WATCHTOWER_NOTIFICATION_REPORT=true
Step 3: Enable Auto-Updates on Target Containers
Here is how the opt-in filter shields your applications. In this sample docker-compose.yml, we run two services: an Uptime Kuma monitoring dashboard and a MariaDB database server.
services:
  uptime-kuma:
    image: louislam/uptime-kuma:1
    container_name: uptime-kuma
    restart: unless-stopped
    ports:
      - "3001:3001"
    volumes:
      - ./kuma-data:/app/data
    labels:
      # Opt-in to automatic updates
      - "com.centurylinklabs.watchtower.enable=true"

  mariadb:
    image: mariadb:10.11
    container_name: production-db
    restart: unless-stopped
    environment:
      - MYSQL_ROOT_PASSWORD=SuperSecretPasswd
    volumes:
      - ./db-data:/var/lib/mysql
    labels:
      # Excluded from auto-updates (redundant with opt-in, but good practice)
      - "com.centurylinklabs.watchtower.enable=false"
Notice the label keys. Watchtower scans Uptime Kuma every morning at 4:00 AM, pulling bug fixes seamlessly. Meanwhile, MariaDB remains locked on version 10.11. Watchtower skips it entirely, protecting raw InnoDB tables from unexpected format upgrades.
Step 4: Launch and Test the Notification Pipeline
Start the Watchtower stack in detached mode:
docker compose up -dNever wait until 4:00 AM to verify your notification setup. Test your bot immediately with an ephemeral container using the --run-once flag:
docker run --rm \
  -v /var/run/docker.sock:/var/run/docker.sock \
  -e WATCHTOWER_NOTIFICATIONS=shoutrrr \
  -e WATCHTOWER_NOTIFICATION_URL="telegram://7123456789:AAEk9_exampleTokenStringXYZ123@telegram?channels=987654321" \
  -e WATCHTOWER_NOTIFICATION_REPORT=true \
  containrrr/watchtower:latest --run-once
Unlock your phone and open Telegram. Within 5 to 10 seconds, your bot will post a diagnostic report listing scanned containers and skipped targets. If an update was applied, the alert will include the container name, the old image hash, and the new SHA-256 digest.
Wrapping Up: A Resilient Update Strategy
A reliable HomeLab balances hands-free convenience with rock-solid stability. Pairing Watchtower’s opt-in labels with instant Telegram alerts eliminates monotonous update chores while keeping you in full control.
Three core rules keep your homelab healthy as it scales:
- Store persistent application state on dedicated host volumes.
- Back up Compose files and databases before every manual upgrade.
- Enable auto-updates exclusively on lightweight, stateless workloads.
Configure it once, let Watchtower handle the minor bumps, and enjoy your weekend uninterrupted.