The Pain of Remote Microservice Debugging
You push a one-line bug fix to staging. Then you wait 12 minutes for CI to compile the binary, build a 650 MB Docker image, and run deployment checks. When the pod finally starts, the service crashes immediately. A missing Vault secret or an unresolvable internal DNS record killed it. The traditional loop—add print statements, commit, wait for CI/CD, tail logs—burns hours of engineering time every single sprint.
The underlying culprit is environment drift. Modern microservices don’t run in a vacuum.
A typical backend service relies on CoreDNS, Istio sidecars, AWS IAM roles for service accounts (IRSA), managed Redis instances, and mounted Kubernetes secrets. Replicating that entire web of infrastructure locally using Docker Compose or Minikube requires hundreds of lines of brittle YAML that drifts out of date within weeks. You need your IDE debugger attached directly to live cluster traffic—without having to deploy halfway-tested code to see if it works.
How Developers Bridge Local Code and Kubernetes
Engineering teams typically turn to three distinct strategies to bridge the gap between their workstation and a remote cluster.
1. The Build-Push-Deploy Loop
Every code change triggers a container build, registry push, and rolling update. While automated tooling like Skaffold or Tilt can cut iteration times down to 2–3 minutes, that delay still interrupts deep focus. Multiply that lag across twenty minor adjustments during an afternoon incident, and you lose over an hour just waiting on Docker daemons.
2. Traffic Proxies (Telepresence & Port-Forwarding)
Running kubectl port-forward handles outbound calls to a single pod, but it won’t resolve cluster-internal hostnames like order-db.staging.svc.cluster.local, nor can other cluster services reach your machine.
Two-way proxy tools like Telepresence solve this by swapping the remote deployment with a routing proxy pod. However, swapping live deployments alters cluster state, requires broad cluster-admin permissions, and frequently disrupts teammates who are running QA checks on that same shared namespace.
3. Process-Level Syscall Interception (mirrord)
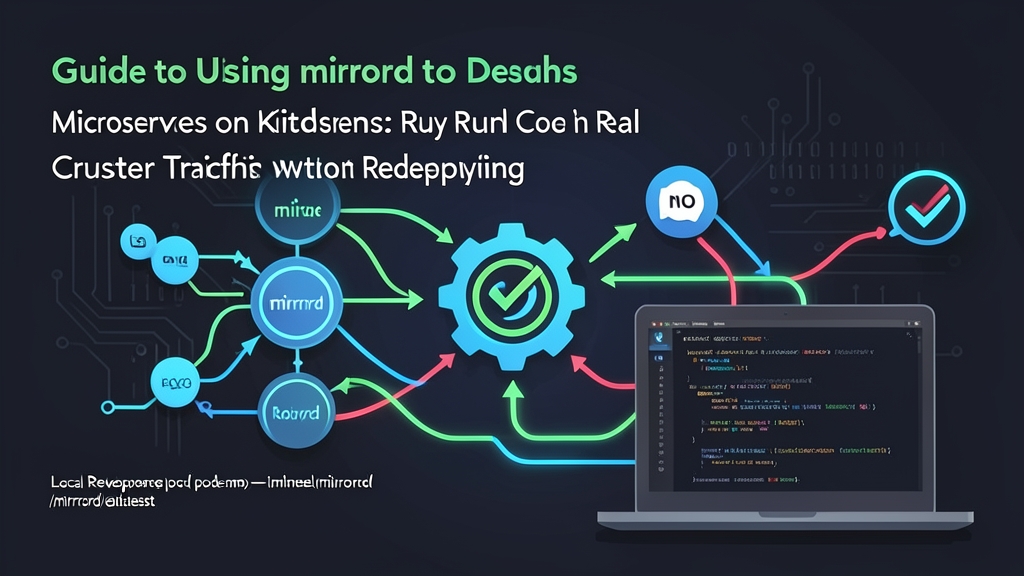
mirrord sidesteps container redeployments entirely. Instead of replacing pods, it hooks into your application process right on your development machine using LD_PRELOAD on Linux or dynamic loader hooks on macOS.
At the same time, mirrord launches an ephemeral, low-privilege agent pod (or ephemeral container) alongside your target workload in the cluster. Whenever your local code initiates a network call, asks for an environment variable, or reads a file, mirrord intercepts the syscall locally and proxies it through the cluster agent.
Pros & Cons of mirrord
Pros
- Zero cluster mutation: mirrord deploys a temporary agent that consumes roughly 15–30 MB of memory and vanishes as soon as you stop debugging. It never modifies your deployment manifests, service definitions, or replica counts.
- Real traffic mirroring: In duplicate mode, mirrord copies incoming TCP and HTTP packets directly from your target pod to your local port. The actual cluster pod continues serving staging traffic without missing a beat.
- Automatic context injection: Environment variables, mounted secrets, and ConfigMaps resolve automatically without needing manual
.envfile maintenance. - Non-blocking breakpoints: Pause execution inside VS Code, GoLand, or IntelliJ for 10 minutes to inspect memory. The real pod continues processing live cluster requests without throwing 504 gateway timeouts to upstream callers.
- Staging stability: Multiple developers can tap into the same shared staging namespace simultaneously without stepping on each other’s toes or corrupting cluster state.
Cons
- Risk of duplicate database writes: When mirroring traffic blindly, write operations execute twice—once on the live pod and once on your local machine. You must use traffic stealing with HTTP header filters for stateful workflows to avoid duplicate database entries.
- Go runtime syscall interception: Go programs bypass standard C runtime libraries (
libc) and issue raw kernel syscalls directly. To intercept these, mirrord must patch binary instructions in memory or useptrace, which adds slight overhead during intensive I/O operations. - RBAC constraints: Developers still need Kubernetes permissions to spawn ephemeral containers or create jobs/pods inside the target namespace.
Recommended Setup: Selective Traffic Stealing
On shared staging clusters, configure mirrord to steal only targeted debug requests while leaving general traffic alone. Combine this with read-only remote filesystem access so your process reads live configuration without altering shared storage.
This configuration delivers four key safeguards:
- Your local process intercepts only requests tagged with your custom HTTP header (such as
x-debug-session: true). - Regular test traffic from CI pipelines and QA engineers continues reaching the real pod uninterrupted.
- Secrets and configuration files read directly from remote pod volume mounts at runtime.
- Database writes happen once, safely scoped to your specific debug session.
Save this configuration as .mirrord/mirrord.json in your project root:
{
  "$schema": "https://raw.githubusercontent.com/metalbear-co/mirrord/main/mirrord-schema.json",
  "target": {
    "path": {
      "deployment": "payment-service"
    },
    "namespace": "staging"
  },
  "feature": {
    "network": {
      "incoming": {
        "mode": "steal",
        "http_filter": {
          "header_filter": "x-debug-session: true"
        }
      },
      "outgoing": true,
      "dns": true
    },
    "fs": {
      "mode": "read"
    },
    "env": true
  }
}
Implementation Guide: Debugging a Service Step-by-Step
Step 1: Install the mirrord CLI
Install the binary on your development machine using the official install script or package manager:
# Linux and macOS install script
curl -fsSL https://inputs.metalbear.co/mirrord/install.sh | bash

# Or via Homebrew on macOS
brew install metalbear-co/mirrord/mirrord
Confirm the binary works and check your installed version:
mirrord --versionStep 2: Authenticate with Your Kubernetes Context
mirrord uses your active ~/.kube/config credentials. Check your target cluster context and verify the target pod is healthy:
kubectl config current-context
kubectl get pods -n staging -l app=payment-service
Step 3: Run Your Local Process in the Cluster Context
Launch your local code through mirrord instead of building a container image. mirrord attaches to the local process, starts the cluster agent, and wires up I/O redirection automatically:
# Running a Python FastAPI service locally
mirrord exec --config-file .mirrord/mirrord.json -- uvicorn app:app --port 8080

# Or running a Node.js microservice
mirrord exec --config-file .mirrord/mirrord.json -- npm run dev
During startup, the CLI confirms the connection details:
mirrord: connected to target deployment/payment-service in namespace staging
mirrord: ready to mirror network traffic and forward environment variables
[Local Server] Running on http://localhost:8080
Step 4: Verify Environment and Cluster Resolution
Test that your local process accesses internal Kubernetes resources without any local port-forwarding tunnels configured:
import os
import requests

# Hostname resolves directly through Kubernetes CoreDNS
DB_HOST = os.getenv("DATABASE_HOST", "postgres.internal.svc.cluster.local")
API_KEY = os.getenv("PAYMENT_GATEWAY_SECRET")

def check_status():
    print(f"Database host from pod env: {DB_HOST}")
    print(f"Secret injected from cluster: {API_KEY[:4]}****")

    # Outgoing call exits from the cluster agent pod, inheriting its security groups and network policies
    resp = requests.get("http://auth-service.staging.svc.cluster.local/health", timeout=5)
    print(f"Auth service health status: {resp.status_code}")

if __name__ == "__main__":
    check_status()
Step 5: Testing with Filtered Traffic
Send two distinct curl requests to your staging ingress endpoint to test the header filter:
# 1. Standard request: passes directly to the remote Kubernetes pod
curl -X POST https://staging.example.com/api/v1/payments \
  -H "Content-Type: application/json" \
  -d '{"amount": 49.99}'

# 2. Debug request: stolen and routed straight to your local debugger
curl -X POST https://staging.example.com/api/v1/payments \
  -H "Content-Type: application/json" \
  -H "x-debug-session: true" \
  -d '{"amount": 49.99}'
Your local debugger catches the second request immediately. You can step through functions, inspect memory, and verify fixes against live services in seconds—no Docker rebuilds, no image pushes, and no pod restarts required.