Skip to content
ITNotes ITNotes

From Terminal to Cloud

  • AI
  • DevOps
  • HomeLab
  • Linux
  • Networking
  • Programming
  • English
    • English
    • Tiếng Việt
    • 日本語
  • AI
  • DevOps
  • HomeLab
  • Linux
  • Networking
  • Programming
  • English
    • English
    • Tiếng Việt
    • 日本語
Home » Web Security
Security tutorial - IT technology blog
Posted inSecurity

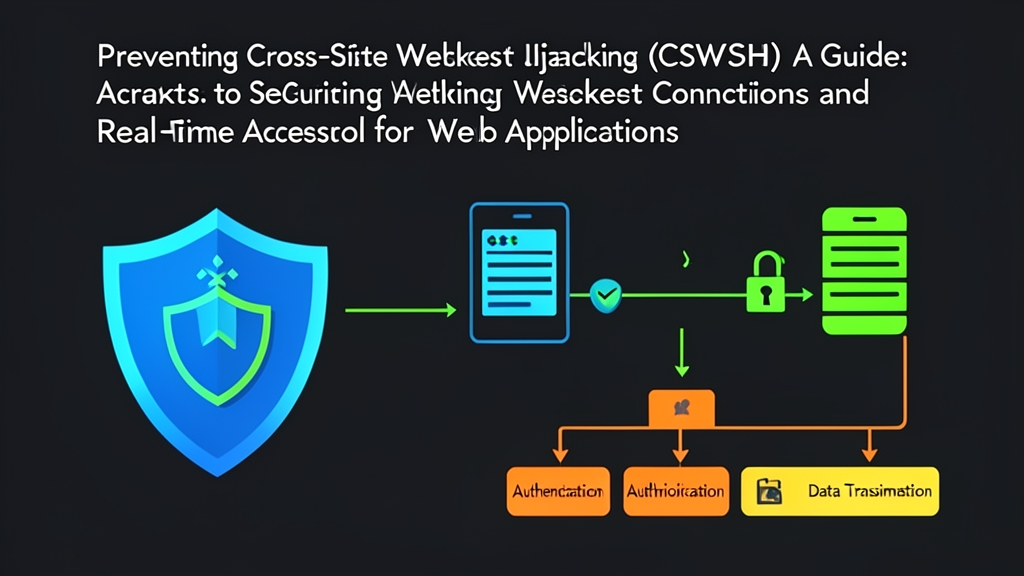
Preventing Cross-Site WebSocket Hijacking (CSWSH): Securing Real-Time Connections

October 18, 2026
Cross-Site WebSocket Hijacking (CSWSH) allows malicious websites to hijack authenticated real-time data feeds. Discover how to inspect the Origin header, implement one-time tickets, and configure reverse proxies to keep WebSocket connections secure.
Read More
Security tutorial - IT technology blog
Posted inSecurity

Deploying ModSecurity and OWASP CRS on Nginx: Open-Source WAF Setup

October 15, 2026
Deploy ModSecurity v3 and OWASP CRS v4 on Nginx to block zero-day probes and OWASP Top 10 exploits. Includes dynamic module builds, anomaly scoring setup, and live verification.
Read More
Security tutorial - IT technology blog
Posted inSecurity

Hardening Nginx with Content Security Policy (CSP) and HTTP Security Headers

October 15, 2026
When an unauthenticated injection triggered a 2 AM emergency, missing HTTP headers left customer browsers wide open. Here is how to configure Content Security Policy (CSP), X-Frame-Options, and HSTS directly in Nginx to block XSS and clickjacking.
Read More
Security tutorial - IT technology blog
Posted inSecurity

Beyond the Wildcard: Stop CORS Misconfigurations from Leaking User Data

September 11, 2026
CORS misconfigurations are a primary vector for session theft. Learn how to move from dangerous 'Allow-All' setups to a secure, allowlist-based implementation for production APIs.
Read More
Security tutorial - IT technology blog
Posted inSecurity

Beyond the Firewall: Stopping Mass Assignment and IDOR in Modern APIs

September 11, 2026
API security isn't just about encryption. Learn how to defend against Mass Assignment and IDOR attacks using Object-Level Access Control and strict data validation.
Read More
Security tutorial - IT technology blog
Posted inSecurity

HTTP Request Smuggling: Breaking the Chain Between Proxies and Backends

August 26, 2026
Discover how HTTP Request Smuggling exploits discrepancies between proxies and backends. Learn to identify CL.TE and TE.CL vulnerabilities and how to secure your stack using HTTP/2 and hardened proxy configurations.
Read More
Security tutorial - IT technology blog
Posted inSecurity

Killing XXE and SSTI: A Field Guide to Hardening Web Apps

July 5, 2026
A technical deep-dive into patching XXE and SSTI vulnerabilities. Learn from a real-world incident response scenario to secure your XML parsers and template engines.
Read More
Security tutorial - IT technology blog
Posted inSecurity

Practical Web Security: Hunting XSS, SQLi, and IDOR with Burp Suite Community

June 5, 2026
Learn how to use Burp Suite Community Edition to secure your web apps. This practical guide covers proxy setup and manual testing for XSS, SQL Injection, and IDOR.
Read More
Security tutorial - IT technology blog
Posted inSecurity

Threat Modeling with STRIDE: Analyze Security Risks Before Writing a Single Line of Code

May 29, 2026
STRIDE threat modeling helps you identify security risks in web apps and APIs before writing code — catching authentication flaws, privilege escalation, and data leaks at the design stage. This guide walks through practical tools like OWASP Threat Dragon and pytm, with real examples for REST API architectures.
Read More
Security tutorial - IT technology blog
Posted inSecurity

Manual Web Forensics: Hunting SQLi and Web Shells via CLI Logs

May 17, 2026
Master manual web forensics using Linux CLI tools like grep and awk to detect SQL injection and hidden web shells in your server logs during an incident.
Read More

Posts pagination

1 2 Next page
Copyright 2026 — ITNotes. All rights reserved.
Privacy Policy | Terms of Service | Contact: [email protected] DMCA.com Protection Status
Scroll to Top