Quick Start: Get Teleport Running in Under 5 Minutes
Traditional SSH key management has a fundamental problem — those keys live forever unless you remember to rotate them. I’ve seen production servers where the authorized_keys file still had keys from engineers who left two years prior. Teleport replaces static credentials with short-lived certificates that expire automatically, and getting it up takes about five minutes on a fresh server.
Install Teleport and generate an initial config in one go:
# Install Teleport (adjust version as needed)
curl https://goteleport.com/static/install.sh | bash -s 15.0.0

# Verify
teleport version

# Generate a basic config with ACME TLS (Let's Encrypt)
sudo teleport configure \
  --cluster-name=mycompany.example.com \
  --public-addr=teleport.mycompany.com:443 \
  --acme [email protected] > /etc/teleport.yaml

# Start the service
sudo systemctl enable teleport --now
sudo systemctl status teleport
Create your first admin user. Teleport prints a signup URL — open it to set a password and configure TOTP or hardware key MFA:
sudo tctl users add admin --roles=editor,access --logins=root,ubuntuThen connect from your workstation:
# Install tsh (macOS: brew install teleport)
# Linux: same curl install command above

tsh login --proxy=teleport.mycompany.com --user=admin
tsh ssh root@your-server
That’s the full loop. No VPN, no long-lived keys, and every session is logged automatically.
Deep Dive: Certificates, Architecture, and RBAC
How the Certificate Lifecycle Works
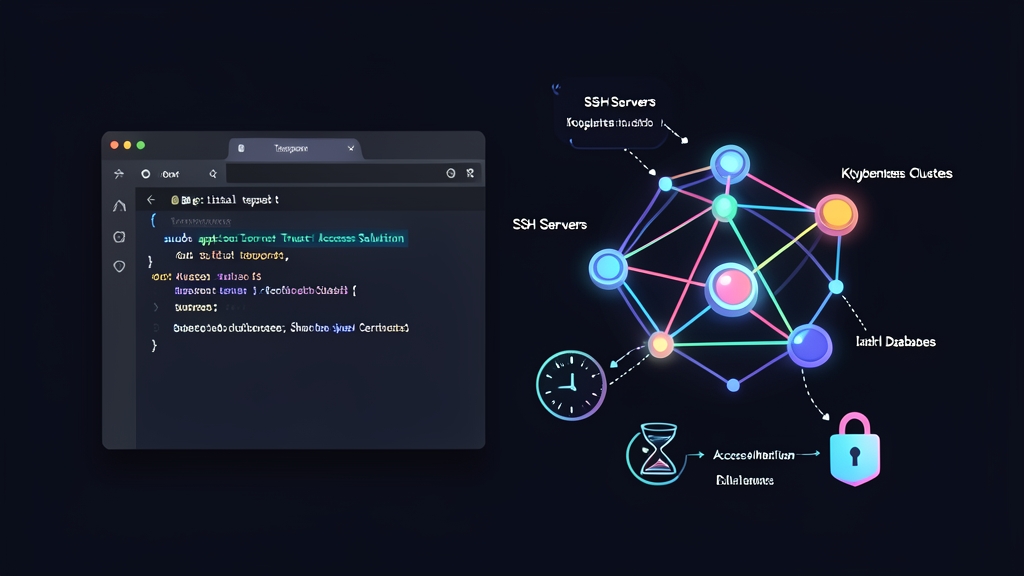
When you run tsh login, Teleport’s Auth Server issues you a certificate with a default TTL of 12 hours. After that window closes, the cert is worthless — there’s nothing to revoke because it already expired. For sensitive environments, you can shorten this to 1–4 hours or require re-authentication per session.
The three main components you need to understand:
- Auth Server — issues certificates, owns the audit log, manages roles and users. Keep this off the public internet.
- Proxy Server — the public-facing entry point, handles TLS termination and the Web UI.
- Node/Agent — a small Teleport process running on each SSH target. It validates certificates locally without calling home.
For production, run Auth and Proxy on separate machines. The node agents are stateless and cheap — throw one on every server you want to protect.
Registering Existing Servers
# On the Auth Server: generate a one-time join token
sudo tctl tokens add --type=node --ttl=1h
# Note the token output

# On the target server: install Teleport, configure as node-only
sudo teleport configure \
  --roles=node \
  --token=<token-from-above> \
  --auth-server=teleport.mycompany.com:443 > /etc/teleport.yaml

sudo systemctl enable teleport --now
Role-Based Access Control That Actually Makes Sense
RBAC is where the day-to-day value shows up. Here’s a typical setup — developers get staging access, ops get prod access with mandatory MFA re-verification:
# /etc/teleport-roles.yaml
kind: role
version: v7
metadata:
  name: dev-access
spec:
  allow:
    logins: ["ubuntu", "ec2-user"]
    node_labels:
      env: ["dev", "staging"]
  deny:
    node_labels:
      env: ["prod"]
  options:
    max_session_ttl: 8h
---
kind: role
version: v7
metadata:
  name: prod-access
spec:
  allow:
    logins: ["ubuntu"]
    node_labels:
      env: ["prod"]
  options:
    max_session_ttl: 4h
    require_session_mfa: true
# Apply both roles
sudo tctl create -f /etc/teleport-roles.yaml
# Assign to users
sudo tctl users update alice --set-roles=dev-access
sudo tctl users update bob --set-roles=prod-accessAdvanced Usage: Kubernetes and Database Access
kubectl Through Teleport — No Exposed API Server Required
Getting Kubernetes access through Teleport means your cluster API server doesn’t need a public IP. Add this to /etc/teleport.yaml on a host with cluster access:
kubernetes_service:
  enabled: yes
  kube_cluster_name: production-k8s
sudo systemctl restart teleport
# On your workstation
tsh login --proxy=teleport.mycompany.com
tsh kube login production-k8s
# kubectl now works — every command is in the audit log
kubectl get pods -n productionEvery kubectl exec, every port-forward — all recorded with the user identity attached. When something breaks at 2am and you need to know what changed, the audit trail is already there.
Database Access Without Distributing Credentials
Teleport proxies PostgreSQL, MySQL, MongoDB, and others. The database connection details stay on the server; developers authenticate through Teleport and never see the actual password:
# /etc/teleport.yaml — on a host with network access to your DB
db_service:
  enabled: "yes"
  databases:
    - name: "prod-postgres"
      description: "Production PostgreSQL"
      protocol: "postgres"
      uri: "postgres-internal.vpc:5432"
      static_labels:
        env: "prod"
# Connect as a developer
tsh db login prod-postgres
tsh db connect prod-postgres --db-user=readonly --db-name=appdb
# Or use your existing psql client via a local proxy
tsh proxy db prod-postgres --port=15432 &
psql "host=localhost port=15432 user=readonly dbname=appdb"Practical Tips from Running This in Production
Use DynamoDB or etcd as the Backend — From Day One
SQLite (the default) works fine for a single-node test setup. The moment you want HA or expect more than a handful of concurrent sessions, switch early:
storage:
  type: dynamodb
  region: ap-northeast-1
  table_name: teleport-backend
  audit_sessions_uri: s3://my-teleport-audit-bucket
Enable Session Recording by Default
Add this to your cluster’s auth spec or base role. You’ll want it the first time you’re debugging a production incident and need to replay exactly what happened:
options:
  record_session:
    default: best_effort
Machine ID for CI/CD Pipelines
Non-interactive services like GitHub Actions or Jenkins need access too. Use tbot instead of hard-coding credentials:
# Create a bot identity
sudo tctl bots add ci-pipeline --roles=deploy-access

# On the CI runner, start tbot
tbot start \
  --auth-server=teleport.mycompany.com:443 \
  --token=<bot-join-token> \
  --destination-dir=/tmp/teleport-certs \
  --certificate-ttl=1h
The pipeline gets fresh certificates every hour with zero manual intervention. No static service account keys sitting in environment variables.
Plan for CA Rotation
Teleport’s own CA certificates have a long lifespan but eventually need rotation. Check expiry regularly and use the graceful rotation flag so existing sessions aren’t dropped:
# Check CA status and expiry
sudo tctl status

# Rotate with a 24-hour overlap window
sudo tctl auth rotate --grace-period=24h
Strong Credentials for the Initial Admin Account
Teleport handles most credential lifecycle automatically, but the master admin password you set during initial setup still matters. When I’m generating passwords for infrastructure access, I use the password generator at toolcraft.app/en/tools/security/password-generator — it runs entirely in the browser, so no data is ever sent over the network. For something protecting your whole cluster’s admin access, that isolation matters. Store the result in a proper password manager immediately.
After running Teleport for a few months, the biggest practical win turns out not to be the Zero Trust security model — though that’s genuinely better than what it replaces. It’s the audit log. When a developer swears they didn’t touch a production server and you can pull up a 30-second session replay that shows exactly what ran, conversations get shorter and postmortems get more honest.